Cisco ACI Features and Benefits: 18 Key Capabilities
Modern enterprise data centers require scalable, secure, and automated network infrastructure. However, managing complex networks across physical servers, virtual machines, and containerized applications can be challenging.
Cisco Application Centric Infrastructure (ACI) addresses these challenges through policy-based networking, centralized management, and automation.
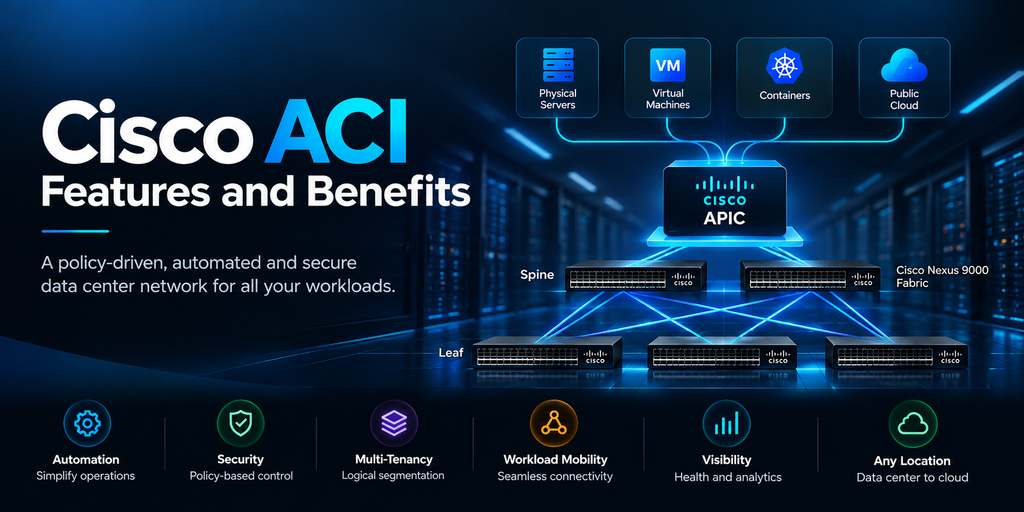
Built on Cisco Nexus 9000 switching infrastructure, Cisco ACI uses the Application Policy Infrastructure Controller (APIC) to manage network policies and fabric operations.
In this article, we explore the key Cisco ACI features and benefits, including microsegmentation, multi-tenancy, workload mobility, network automation, and data center connectivity.
Furthermore, we explain how these capabilities can help organizations simplify network operations, improve security, and support evolving application requirements.
Whether you are a network engineer, data center architect, or IT decision-maker, understanding Cisco ACI architecture can help you evaluate its suitability for your enterprise infrastructure.
One Network for Multiple Workload Types
One of the key Cisco ACI benefits is its ability to provide consistent network policies across supported physical, virtual, and containerized workloads.
As a result, organizations can reduce operational complexity and manage application connectivity through a unified policy framework.
Furthermore, centralized policy management helps network teams maintain consistency as infrastructure requirements evolve.
Centralized Fabric Management
Cisco ACI uses the Application Policy Infrastructure Controller (APIC) to manage fabric policies and network operations.
Through APIC, administrators can configure network policies, monitor fabric health, and troubleshoot connectivity issues.
Additionally, REST APIs enable integration with automation platforms and external management tools.
Consequently, IT teams can streamline repetitive operations and improve operational consistency.
Multi-Tenancy and Network Segmentation
Multi-tenancy is another important feature of Cisco ACI architecture.
For example, organizations can create separate tenants for production, testing, and development environments.
Moreover, tenants can contain their own networking and policy constructs, helping teams organize application environments.
As a result, administrators can manage multiple logical environments while maintaining appropriate isolation through correctly configured VRFs, bridge domains, and security policies.
Embedded Fabric Security
Cisco ACI supports policy-based security using endpoint groups and contracts.
By default, communication between endpoint groups is restricted unless permitted by the applicable policy model and contracts.
Therefore, administrators can define which application components are allowed to communicate.
In addition, properly designed segmentation policies can help limit unnecessary east-west traffic.
However, organizations must carefully configure contracts, endpoint classification, and exceptions to achieve their intended security posture.
Microsegmentation for Application Security
Microsegmentation helps organizations apply more granular security policies to supported workloads.
For instance, administrators can separate application tiers and control communication between workload groups.
Furthermore, Cisco ACI can integrate with supported security services to provide additional traffic inspection.
As a result, organizations can reduce unnecessary connectivity and strengthen application-level security.
Nevertheless, successful implementation requires accurate workload identification, dependency mapping, and ongoing policy validation.
Conclusion: Are Cisco ACI Features and Benefits Right for Your Enterprise?
Cisco ACI provides a policy-driven approach to modern data center networking. By combining centralized management, automation, segmentation, and application-aware policies, it helps organizations manage complex network environments more consistently.
Furthermore, key Cisco ACI features and benefits, such as multi-tenancy, microsegmentation, workload mobility, and programmable infrastructure, can support enterprise requirements for security, scalability, and operational efficiency.
In addition, Cisco ACI enables organizations to standardize network policies across supported data center architectures. As a result, IT teams can simplify routine operations and improve visibility into network health.
However, adopting Cisco ACI requires careful planning. Organizations should evaluate existing infrastructure, application dependencies, licensing, migration complexity, operational skills, and future cloud strategies before implementation.
Therefore, the best approach is to assess Cisco ACI against your business requirements, technical architecture, and long-term infrastructure roadmap.
Ultimately, Cisco ACI can be a strong option for enterprises seeking automated and policy-driven data center networking. Nevertheless, the right solution depends on your organization’s specific use cases and operational needs.
Planning a Cisco ACI Deployment or Data Center Transformation?
Designing a secure and scalable data center network requires more than selecting the right technology.
TREZBON TECHNOLOGIES supports organizations with enterprise network consulting, infrastructure design, solution evaluation, and implementation planning.
Whether you are evaluating Cisco ACI, modernizing your data center, or reviewing your network architecture, our team can help you assess the available options against your technical and business requirements.
Connect with TREZBON TECHNOLOGIES to discuss your enterprise networking requirements.
🌐 https://www.trezbon.com/contact
Related Reading
Explore our article on Software-Defined and Traditional Networking to understand how software-defined networking differs from traditional network architectures.
From Certification to Production: What the Aviatrix ACE Teaches About Multicloud Transit

VeloCloud Licensing, Support & BOQ: Complete SD-WAN Guide

AI-Powered Firewall Troubleshooting: GraphRAG, Neo4j, RAG & Network Automation
About Author

Muhammad Marakkoottathil(MM)
Expert in the field of SDN, cloud computing, virtualization, active-active data center design & migration. Passionate about helping organizations to achieve their digital transformation objectives with strong 15+ years of experience in design, deployment, and managing heterogeneous network solutions across the industry verticals. Major Industry Certifications: Cisco CCIE, CCDP, VMware VCAP-NV_DESIGN, TOGAF, ITIL, NUTANIX NCSE, Google Cloud Architect, Azure Fundamentals More info please visit my page @ LinkedIn: https://www.linkedin.com/in/contactmm/