In this NSX-T Series: Part 3 – Planning NSX VXLAN blog, we will discuss more on the Planning of NSX VXLAN, and what are the pre-requisite which should be collected and planned. But if you want to start from beginning you can refer my previous part of the SeriesNSX-T Series : Part 1 -Architecture and
NSX-T Series : Part 1 -Architecture and Deploy Topology: Intro In part-1 of the series, we discussed how to deploy the NSX manager and this is the: NSX-T Series: Part 2 – Adding Compute Manager. using this, I will take you through how to add vCenter and to pull the inventory. What is Compute Manager
Since the beginning of NSX-T development, it was clear that it will have extensive support for the Multi-Cloud environment, Container, and even can fit into the Telco environment. In this blog: NSX-T Series: Part 1 -Architecture and Deploy, we will explore some key aspects of NSX-T Since I had contributed earlier with VMware Engineering, I
As cyber threats continue to evolve, protecting enterprise networks requires more than traditional firewalls and basic access controls.
Every day, employees and business applications connect to websites, cloud services, and external internet resources. While most of these connections support legitimate business activities, some may lead to malicious websites, phishing pages, malware distribution platforms, or other potentially
As enterprise data centers become more virtualized, managing network connectivity and security across different workloads is becoming increasingly important.
Traditional networking relies heavily on physical switches, VLANs, and hardware-based configurations. While these technologies remain essential, they can introduce operational complexity when organizations need to deploy new applications, connect virtual machines, or make frequent changes to their
In my experience with VMware technology, I would prefer to get first hands-on with VMware HOL https://labs.hol.vmware.com/. This will bring confidence as well as you can get ideas to design in your VMware home lab. Building a Vmware home lab is always fun as you come across with a different set of issues. When I
As enterprise data centers become more complex, protecting applications and workloads from cyber threats has become a major priority for IT and security teams.
Traditionally, organizations focused on securing their network perimeter using firewalls, intrusion prevention systems, and other security technologies. While these controls remain important, they may not provide sufficient protection against threats that move
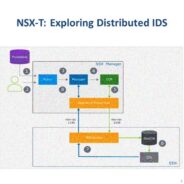
Using this blog “NSX-T: Exploring Distributed IDS” let’s examine distributed IDS features introduced part of NSX 3.0. and we will explore its architecture and key configuration details. Distributed intrusion detection uses network introspection to identify malicious intrusion attempts. This results in distributed intrusion detection to protects east-west traffic and detects L4 attacks. In fact, the
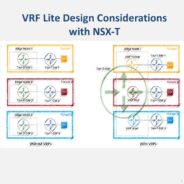
VRF-Lite is the latest capability added part of the NSX-T 3.0 release. Through this blog post “NSX-T 3.0 design consideration for VRF-lite”, let’s explore the benefits of VRF lite and its considerations from design and implementation perspectives. VRF-Lite Advantages Server virtualization admins usually struggle with the core networking concepts like VRF lite. Therefore, I recommend