Cisco ACI Network-Centric vs Application-Centric Design
Cisco ACI Network-Centric vs Application-Centric Design: Which Approach Is Right?
Choosing between Network-Centric vs Application-Centric design is an important decision when implementing Cisco Application Centric Infrastructure (ACI).
However, many organizations struggle to determine which policy model best supports their applications, existing network architecture, and security requirements.
For example, should you migrate existing VLANs directly into Cisco ACI? Or should you design network policies around individual applications and their dependencies?
Furthermore, does Cisco ACI automatically discover applications, identify communication flows, and generate security policies?
The answer depends on the tools, integrations, and design approach used.
Cisco ACI provides flexible policy constructs that support network-centric, application-centric, and hybrid deployment models.
In this article, we compare Network-Centric vs Application-Centric design in Cisco ACI, explain how endpoint groups (EPGs), contracts, and application profiles work, and explore when each approach makes sense.
Additionally, we discuss application dependency mapping, migration considerations, and practical recommendations for enterprise data center environments.

Network vs application-centric is the key design topic whenever you plan for Cisco’s ACI. However, most of the adopters are not very clear about the use cases. The following questions were asked.
- Does ACI automatically capture the application details? also, does it identifies my applications?
- Can ACI automate the application connectivity configurations!
- What is the additional licensing required for application-centric design?
Obviously, the answer to all the above questions is “NO”. Also, I end up clarifying customers on how ACI can be used for doing the policy for their application. Which definitely is one of the differentiators with other SDN solutions. ACI configurations are policy-oriented and when it comes to the policy constructs. On ACI you can use three different methods.
- Network-Centric Approach
- Application-centric approaches.
- Or a combination of network and application-centric
Application Centric Approach
Cisco ACI application network profile (ANP) policy on the APIC controller represents the application, related tiers, and security requirements. The example below shows how a typical three-tier Whatsapp application would be set up with its EPGs( Endpoint Groups). For example, for Whatsapp ANP, it could have EPGs such as WhatsApp’s WEB servers, APP servers, DB servers, etc, and its provider and consumer contracts.
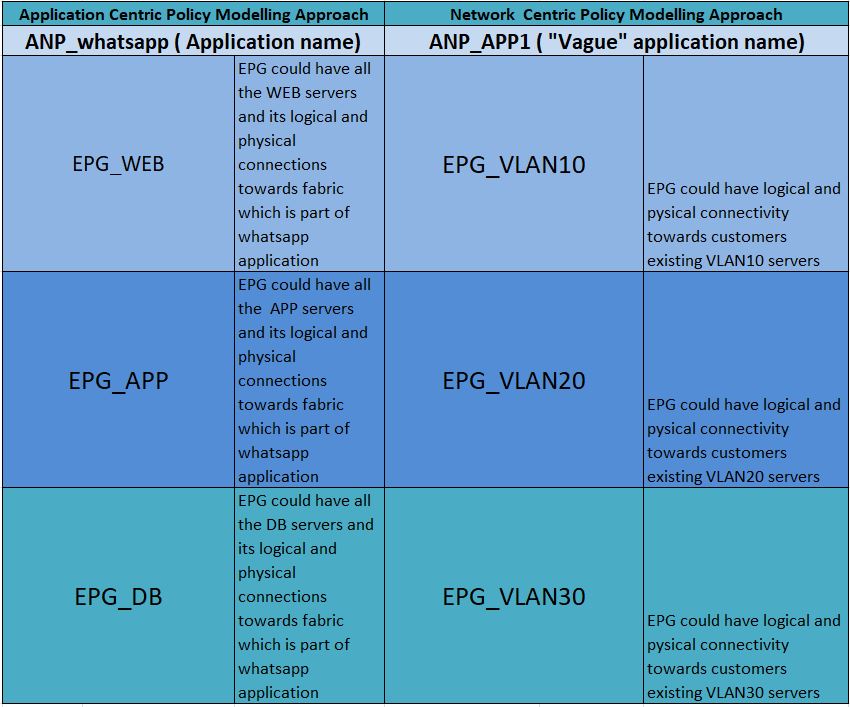
In short, the approach is called application-centric if the policies are created based on application details such as required port-for communication between the tiers, etc. The idea is to give the network administrator a view of the application, its connectivity & security requirements from the ACI controller.
Furthermore for creating ANP, the key requirement is to have the application visibility and its dependencies. If you have Cisco Tetration, it is one of the solutions which could help you to get visibility and application dependency mapping ( ADM) into each of the flows.
Understanding Network-Centric vs Application-Centric Design in Cisco ACI
Cisco ACI provides a policy-driven networking architecture that allows administrators to organize network connectivity and security requirements.
However, organizations can approach policy design in different ways.
First, the network-centric approach organizes policies around existing networking constructs, such as VLANs and subnets.
In contrast, the application-centric approach organizes policies around application components and their communication requirements.
Additionally, organizations can combine both approaches to support gradual infrastructure modernization.
Therefore, selecting the right model depends on application visibility, migration requirements, security objectives, and operational readiness.
1. Application-Centric Approach in Cisco ACI
An application-centric approach organizes network policies according to application requirements rather than relying primarily on traditional network boundaries.
For example, consider a three-tier enterprise application containing web, application, and database servers.
Administrators can create an Application Network Profile (ANP) and associate relevant Endpoint Groups (EPGs) with the application tiers.
As a result, the policy model can represent application components and their communication relationships.
Furthermore, Cisco ACI contracts define which types of traffic are permitted between EPGs.
For instance:
- Web-tier EPG: Handles client-facing application traffic.
- Application-tier EPG: Processes business logic and application requests.
- Database-tier EPG: Stores and manages application data.
In addition, contracts can define the communication permitted between these groups.
However, effective application-centric design requires accurate knowledge of application dependencies.
Therefore, organizations should identify communication flows, protocols, ports, and workload relationships before enforcing restrictive policies.
Application dependency mapping tools can support this process.
Consequently, network teams can create policies that better reflect application requirements while reducing unnecessary connectivity.
2. Network-Centric Approach in Cisco ACI
The network-centric approach organizes Cisco ACI policies around existing networking constructs, including VLANs, subnets, and bridge domains.
Unlike application-centric design, this approach does not require administrators to model every application tier from the beginning.
For example, an organization migrating from a traditional data center network might map existing VLAN-based groups into Cisco ACI EPGs.
A simplified design could include:
- VLAN 10 → EPG-A
- VLAN 20 → EPG-B
As a result, administrators can preserve familiar network groupings during the initial migration.
Furthermore, this approach can reduce the amount of application-level information required at the beginning of the project.
However, administrators must still validate endpoint classification, routing, contracts, and connectivity requirements.
In addition, a network-centric design may provide less granular application segmentation when compared with a carefully designed application-centric model.
Nevertheless, it can offer a practical starting point for organizations migrating legacy infrastructure into Cisco ACI.
3. Combining Network-Centric and Application-Centric Design
Organizations do not always need to choose only one Cisco ACI policy model.
Instead, they can adopt a hybrid approach based on application requirements and migration priorities.
For instance, existing applications can initially use network-centric policies, while new applications can adopt application-centric designs.
Meanwhile, network teams can gradually identify application dependencies and refine security policies.
Furthermore, this approach allows organizations to introduce application-aware segmentation without redesigning the entire environment simultaneously.
However, moving from network-centric to application-centric policies requires careful planning.
Depending on the existing architecture, administrators may need to modify EPG membership, policy relationships, contracts, and workload connectivity.
Therefore, a phased migration strategy can help reduce operational risk and improve implementation consistency.
Ultimately, a hybrid approach provides flexibility for enterprises modernizing complex data center environments.
Recommendation
- If there is an option to use Tetration or any other ADM tool use them to create an application profile on ACI
- If the above is not an option – make it as simple as VLAN to EPG mapping
Conclusion: Network-Centric vs Application-Centric — Choosing the Right Cisco ACI Design
Choosing between Network-Centric vs Application-Centric design is not simply about selecting one policy model over another. Instead, the decision should reflect your organization’s application requirements, existing infrastructure, security objectives, and migration strategy.
On one hand, a network-centric approach provides a practical starting point for organizations migrating traditional VLAN-based networks into Cisco ACI.
On the other hand, an application-centric approach allows network teams to organize policies around application tiers, communication flows, and security requirements.
Furthermore, a hybrid approach enables organizations to combine both models. As a result, enterprises can modernize their data center networks gradually while maintaining appropriate operational controls.
However, successful application-centric design depends on accurate application dependency mapping, effective EPG classification, and properly configured contracts.
Therefore, organizations should evaluate their application visibility, operational capabilities, and migration requirements before selecting a Cisco ACI policy model.
Ultimately, the best Cisco ACI architecture is one that supports your business applications, simplifies network operations, and aligns with your long-term infrastructure strategy.
Planning a Cisco ACI Deployment or Data Center Migration?
Selecting the right policy model is only one part of building a secure and scalable enterprise data center.
TREZBON TECHNOLOGIES supports organizations with enterprise networking consulting, data center architecture assessment, solution evaluation, and infrastructure transformation planning.
Whether you are evaluating Cisco ACI, migrating from traditional networking, or planning application segmentation, our team can help you assess the technical requirements and available design options.
Connect with TREZBON TECHNOLOGIES to discuss your data center networking requirements.
🌐 https://www.trezbon.com/contact
Related Reading
Explore our detailed guide on Cisco ACI Features and Benefits to understand its key capabilities.
For additional technical information, refer to the Cisco ACI documentation and design resources.
NVIDIA DGX SuperPOD: Build a Mini SuperPOD Lab Step by Step
VMware NSX-T and Cisco ACI and Its Complimenting Use Cases
AlgoSec – NSPM Solution Quick Review
About Author

Muhammad Marakkoottathil(MM)
Expert in the field of SDN, cloud computing, virtualization, active-active data center design & migration. Passionate about helping organizations to achieve their digital transformation objectives with strong 15+ years of experience in design, deployment, and managing heterogeneous network solutions across the industry verticals. Major Industry Certifications: Cisco CCIE, CCDP, VMware VCAP-NV_DESIGN, TOGAF, ITIL, NUTANIX NCSE, Google Cloud Architect, Azure Fundamentals More info please visit my page @ LinkedIn: https://www.linkedin.com/in/contactmm/
Good day, Thank you for this article my question is related to a brown fields install where we have a network centric network and needs to move to Application but the servers are all hosted on the same subnet /24. If I created a EPG I need to bind this to the BD and Vrf . Will I then created Web-EPG , APP-EPG and DB-EPG and map all of them to the same BD which points to the the /24 subnet? Or how would I accomplish this maybe using TAGS?
Hi jcv365 – thank of your question. I don’t recommend going for mapping your application tiers to single BD – as the BD is equivalent to a broadcast domain. the best way is to group is your application functions into corresponding EPG/VLAN tag and profile them into one ANP. in your case you need to consider re-subnetting of your /24 multiple chunks according to ur application needs.
I hope it answers your queries.
Muhammad Thanks for this article, My question is by adopting network centric approach do we see any changes in traffic flow as compare to Application centric method ? as per my understanding with network centric approach we define EPG based on Vlan or subnet and we only pass traffic between different EPGs based on layer 3 boundaries/known ports (by defining in contracts), as EPG based on subnet or Vlan so we can’t add different subnet device in EPG . Apart from that there is no difference in Network Centric or Application Centric method traffic flow
Hi Sourabh, if you look at it from a traffic flow perspective usually no difference as the flow design usually based on security requirements – you may send traffic through a firewall or other L4L7 devices independent of whether you do network or application-centric.
regards, MM