ZTNA Platform Comparison 2026 | 11 Zero Trust Solutions
Zero Trust Network Access (ZTNA) has evolved from a VPN replacement technology into a foundational enterprise security architecture in 2026. Traditional VPNs are increasingly viewed as a security liability due to excessive implicit trust, credential theft risks, lateral movement exposure, and poor visibility into third-party access. Modern enterprises now require identity-first, least-privilege access models that validate users and devices before connectivity is established.
ZTNA addresses these challenges by granting access only to explicitly authorized applications rather than exposing entire networks. Mature platforms continuously evaluate identity, device posture, location, and behavioral context throughout the session lifecycle. This architecture aligns closely with compliance frameworks such as NIST SP 800-207, NIST SP 800-171, CMMC 2.0, IEC 62443, HIPAA, GDPR, NIS2, and GCC cybersecurity mandates including NCA ECC v2.0.
In March 2026, Trezbon Technology & Security Advisory published an independent evaluation of eleven major ZTNA platforms focused exclusively on ZTNA capabilities rather than broader SSE or SASE functionality. The assessment covered enterprise IT, hybrid cloud, remote workforce, third-party access, DevOps, and OT/ICS use cases.
ZTNA Platforms Evaluated
| Vendor | Product | Primary Strength |
| Appgate | Appgate SDP | OT/ICS & Microsegmentation |
| Zscaler | ZPA | Large Remote Workforce |
| Cloudflare | Zero Trust | DevOps & Third-Party Access |
| Palo Alto | Prisma Access ZTNA 2.0 | Advanced Policy Enforcement |
| Cisco | Secure Access | SD-WAN Integration |
| Microsoft | Entra Private Access | Microsoft Ecosystem Integration |
| BeyondCorp Enterprise | Google Workspace Security | |
| Akamai | Enterprise Application Access | Clientless Access |
| Netskope | Private Access | Hybrid Cloud Access |
| Fortinet | Fortinet ZTNA | Fortinet Fabric Integration |
| Check Point | Harmony Connect | Compliance & BYOD |
Each platform was evaluated across 12 weighted capability categories using a standardized 1–5 scoring scale. The scoring model emphasized architectural depth, identity-centric access enforcement, microsegmentation, compliance alignment, and support for legacy and OT environments. Weighted scoring reflects real-world enterprise risk priorities rather than marketing feature parity.
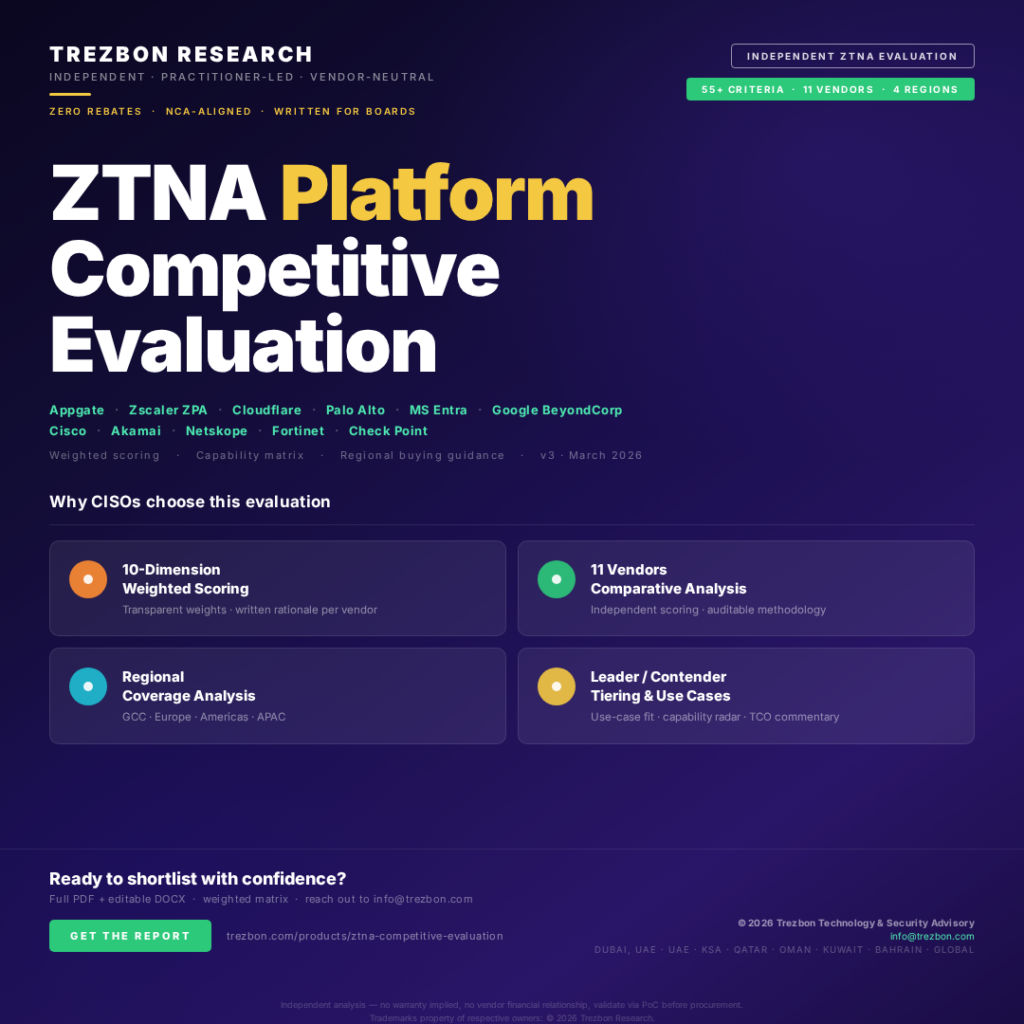
Final Weighted ZTNA Scores (Out of 5.00)
| Vendor | Score | Market Position |
| Appgate SDP | 4.51 | Leader |
| Zscaler ZPA | 4.38 | Leader |
| Cloudflare Zero Trust | 4.22 | Leader |
| Palo Alto Prisma Access | 4.18 | Strong Contender |
| Microsoft Entra PA | 4.14 | Strong Contender |
| Google BeyondCorp | 4.05 | Contender |
| Cisco Secure Access | 3.92 | Contender |
| Akamai EAA | 3.88 | Contender |
| Netskope ZTNA | 3.75 | Contender |
| Fortinet ZTNA | 3.62 | Niche |
| Check Point Harmony Connect | 3.51 | Niche |
Key Findings
Architecture
The report identified architecture as the most important differentiator in the ZTNA market. Direct-routed Software Defined Perimeter (SDP) platforms create secure connections directly between users and applications without forcing traffic through vendor-controlled cloud proxies. This reduces latency, lowers operational costs, improves deterministic performance, and minimizes shared infrastructure exposure.
Appgate SDP was the highest-ranked platform in this category due to its direct-routed architecture and strong hybrid deployment support across cloud, on-premises, and OT environments.
Proxy-based architectures, used by vendors such as Zscaler, Palo Alto, Cisco, and Netskope, provide strong scalability and cloud-delivered access but may introduce additional latency and dependency on vendor cloud infrastructure. .
Cloudflare stood out for its edge-delivered Zero Trust architecture using a global Anycast network, offering excellent performance for DevOps, contractor, and BYOD scenarios.
Microsegmentation Is Critical
The report emphasized that modern ZTNA is no longer just about replacing VPNs. Advanced platforms now enforce per-application and per-session microsegmentation to prevent lateral movement after compromise.
Appgate SDP ranked highest for microsegmentation because of its ability to enforce workload-to-workload restrictions and “segment-of-one” connectivity without proxy overhead. Palo Alto Prisma Access ZTNA 2.0 also scored highly because of its continuous verification and ML-driven policy capabilities.
OT/ICS Support Remains Limited
One of the strongest conclusions from the evaluation was that most ZTNA vendors are not fully prepared for operational technology (OT) and industrial control system (ICS) environments. Industrial sectors require agentless deployment, deterministic performance, protocol transparency, and support for air-gapped environments.
According to the report, Appgate SDP was the only evaluated vendor with production-proven OT/ICS remote access capabilities that do not require cloud dependency or intrusive protocol inspection. This makes it particularly suitable for energy, utilities, manufacturing, oil & gas, and critical infrastructure sectors.
How to Choose a ZTNA Platform in 2026
When evaluating a ZTNA platform, organizations should look beyond basic remote-access features. Instead, assess how each solution fits the existing security architecture, applications, users, and risk requirements.
Start by evaluating identity integration and device posture controls. Next, determine whether the platform provides application-level least-privilege access and limits lateral movement.
In addition, organizations should assess:
- Hybrid and multi-cloud deployment support
- Microsegmentation capabilities
- Third-party and contractor access
- Clientless application access
- Legacy application compatibility
- OT/ICS requirements
- Logging and security visibility
- High availability and resilience
- Compliance requirements
- Integration with existing identity and security platforms
- Deployment complexity
- Licensing and long-term total cost of ownership
Finally, conduct a structured ZTNA proof of concept using real applications, users, network paths, and security policies. This helps validate security controls, user experience, latency, operational complexity, and integration requirements before production deployment.
This also aligns well with NCSC’s current guidance that organizations adapt ZTNA architecture to their environment, objectives, and risk requirements rather than treating one implementation as universally applicable.
Final Thoughts
The 2026 ZTNA market has matured far beyond simple VPN replacement. Leading platforms are now differentiated by architecture depth, identity-aware policy enforcement, microsegmentation capabilities, clientless access maturity, and OT readiness.
Trezbon’s research concludes that organizations should treat ZTNA as a long-term architectural and risk-management decision rather than a feature comparison exercise. Enterprises are advised to conduct structured proof-of-concept testing, validate latency and operational impact, assess compliance requirements, and evaluate long-term TCO before selecting a platform.
For more information or access to the full report, contact Trezbon Technology & Security Advisory at info@trezbon.com. And more blogs on Cybersecurity and related topics, please use the link.
Conclusion: Choosing the Right ZTNA Platform in 2026
Zero Trust Network Access has evolved beyond traditional VPN replacement. Today, enterprises use ZTNA to provide identity-aware, least-privilege access to applications across data centers, cloud environments, remote workforces, and third-party ecosystems.
However, not every ZTNA platform uses the same architecture or delivers the same capabilities. Key differences include identity integration, microsegmentation, application access, deployment architecture, clientless access, hybrid-cloud support, security visibility, and OT/ICS readiness.
Therefore, organizations should evaluate ZTNA as a long-term security architecture decision rather than a simple product comparison.
Before selecting a platform, conduct a structured proof of concept. Test real applications and access scenarios, validate identity and device controls, measure latency, assess operational complexity, and review integration with your existing security infrastructure.
In addition, consider compliance requirements, scalability, resilience, licensing, and long-term total cost of ownership.
Ultimately, the right ZTNA architecture should reduce unnecessary network exposure, enforce least-privilege access, limit lateral movement, and provide consistent access controls across the enterprise.
Need Help Evaluating ZTNA Platforms?
Selecting a ZTNA platform requires more than comparing product features.
TREZBON Technology & Security Advisory helps organizations evaluate ZTNA architectures, compare platforms, design proof-of-concept scenarios, and assess solutions against enterprise security and operational requirements.
Explore the ZTNA Platform Competitive Evaluation Report 2026 and compare leading enterprise ZTNA solutions:
https://trezbon.com/products/ztna-products-comparison
For ZTNA consulting, architecture assessment, or product evaluation:
Evaluating ZTNA for Your Enterprise?
Choosing a ZTNA platform should start with your architecture, users, applications, security requirements, and operational environment—not a vendor feature list.
Access the ZTNA Platform Competitive Evaluation Report 2026 to explore the detailed comparison:
https://trezbon.com/products/ztna-products-comparison
Need help comparing ZTNA platforms or planning a proof of concept?
Talk to TREZBON Technology & Security Advisory:
https://trezbon.com/#contact.
Arista NDR: Architecture, Components & Key Use Cases
Comparing Cisco Tetration with VMware NSX
Securing Internet Access Using Cisco Umbrella
About Author

Trezbon Research
The Trezbon Research Team is a practitioner-led, vendor-neutral group of senior technology experts dedicated to producing high-impact, decision-grade research and technology artefacts for enterprise and regulated industries. Built on deep hands-on experience and advisory excellence, the team transforms complex technology landscapes into clear, actionable insights that enable confident decision-making at the CIO, CISO, and board level.